Midnight Privacy Under the Microscope: Shielded CTO Details Risks and Spartacus Plans
Bob Blessing-Hartley reveals what Midnight's privacy architecture does and does not conceal, shares findings from mainnet activity, and outlines how developers can protect users from transaction tracking, AI coding mistakes, and future cryptographic threats.
By SongMarketCap
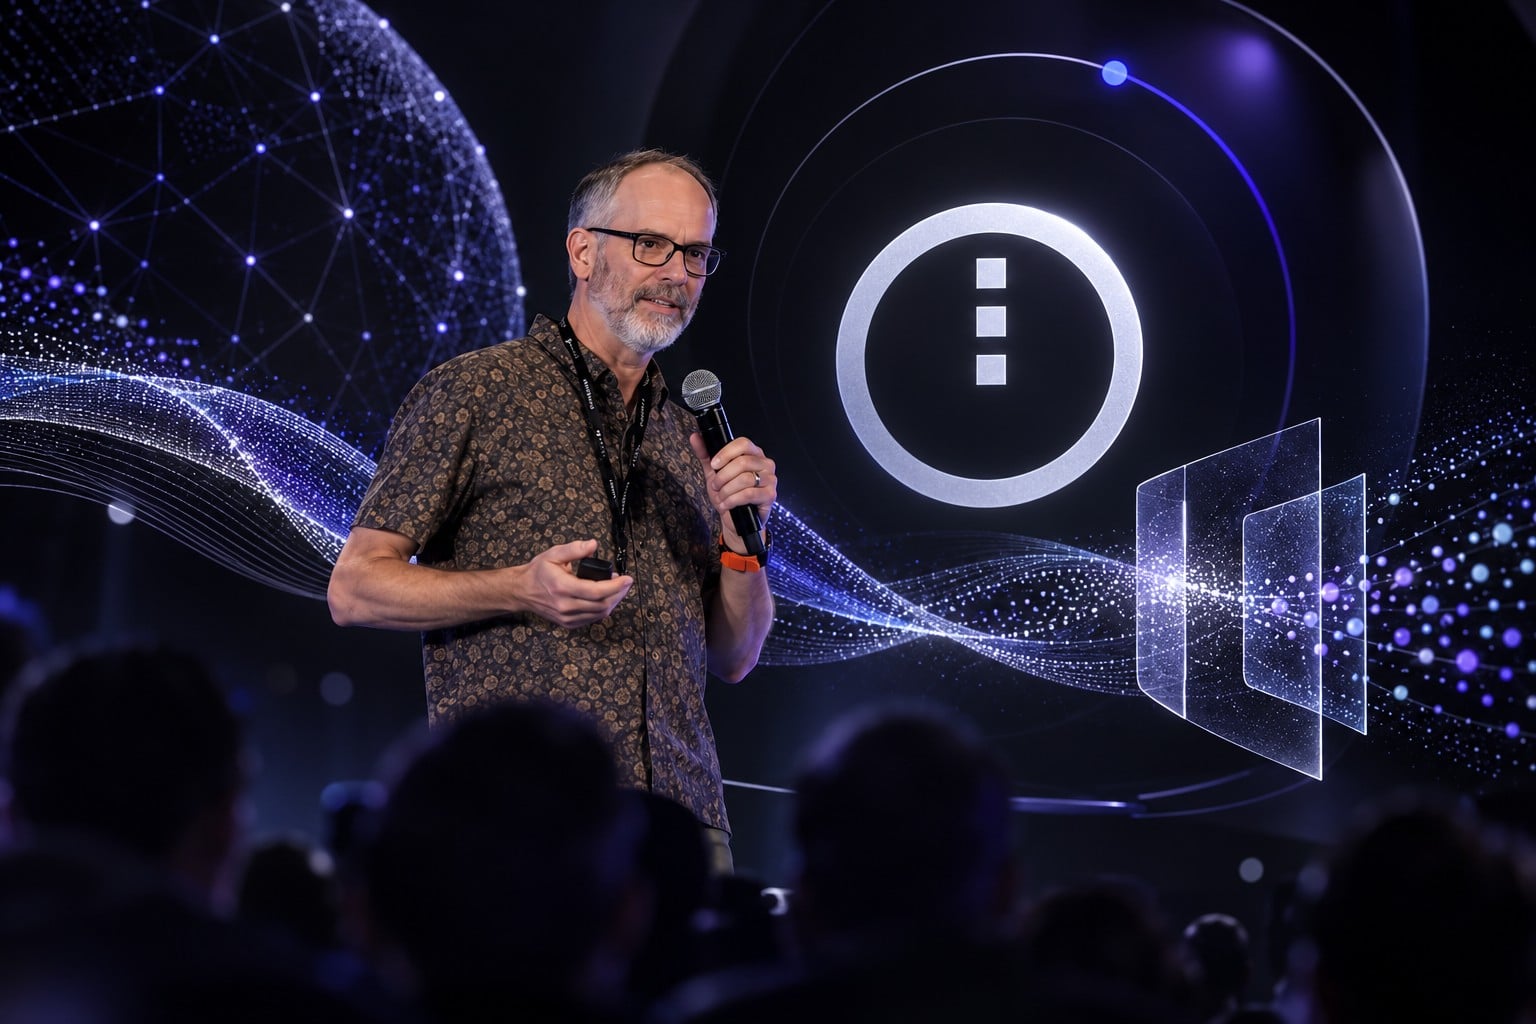
Midnight's zero-knowledge technology can protect sensitive information, but poorly designed applications may still expose their users' behavior. That was the central warning from Bob Blessing-Hartley, CTO of Shielded Technologies, during his Private by Default, Safe by Design presentation at Midnight LIVE.
Speaking to developers, Blessing-Hartley examined how privacy can be weakened through smart contract design, publicly visible metadata, and third-party infrastructure. He also shared findings from Midnight mainnet, including approximately 32,000 shielded coin records and an application that generated 12,754 contract calls in 24 hours.
His presentation went beyond identifying risks. It introduced Spartacus, a planned open-source tool designed to make individual user activity harder to distinguish, alongside recommendations covering AI-assisted development, proof generation, and quantum security.
Private by Default: The Security Rules Every Midnight Developer Should Follow
Blessing-Hartley began with the principle behind Midnight's privacy architecture: sensitive information can remain on a user's device while the blockchain verifies a cryptographic proof.
Age verification provides a straightforward example. Instead of revealing a date of birth, a device generates a zero-knowledge proof confirming that someone meets a required age threshold. The network can verify the claim without receiving the underlying personal information.
However, applications must still verify that claims are trustworthy.
"A name tag is not an ID."
Blessing-Hartley used this comparison to explain why developers cannot automatically trust information supplied by users or locally executed application code. Identity claims and permissions require appropriate verification rather than accepting whatever a device reports.
His second recommendation concerned data minimization.
"Don't overshare."
An application should reveal only what is necessary to complete an operation.
In a decentralized auction, for example, a smart contract might need to establish whether a bid exceeds a minimum amount. A zero-knowledge proof can confirm that condition without revealing whether the actual bid is $5,000 or $50,000.
The same principle applies to verifying membership, eligibility, or other conditions that can be answered with a simple yes or no.
Blessing-Hartley also warned against relying on hashing alone to protect sensitive values. When possible inputs are predictable, observers may test combinations until they find a matching hash.
Adding random salt or padding can make such attacks more difficult, although avoiding unnecessary disclosure remains the preferred approach.
Another concern was the growing use of artificial intelligence to write blockchain applications.
Blessing-Hartley described how AI coding assistants sometimes suggest using Compact's disclose() mechanism when handling private information becomes difficult.
While disclosure has legitimate uses, developers must understand when information crosses a privacy boundary and whether it could become publicly accessible.
He acknowledged seeing such mistakes in hackathon applications, including projects developed by his own team.
To address these weaknesses, Blessing-Hartley recommended maintaining security invariants, a predefined set of requirements that applications must satisfy before deployment.
He explained that his own development workflow includes a protected collection of these rules, with applications assessed against them before publication.
His broader message was that a technically valid smart contract is not necessarily a privacy-preserving one.
What Midnight Mainnet Reveals: Contract Calls, Metadata and 12,754 Transactions
A substantial part of the presentation examined the information that remains visible even when Midnight's privacy mechanisms work as intended.
Blessing-Hartley described the path information follows from a user's device through proof-generation infrastructure and finally to the blockchain.
Private coin records, identity details, and other sensitive information may remain on the device. Proof-generation software processes the necessary private inputs and produces cryptographic evidence for network verification.
However, outside services can introduce additional exposure.
Remote proof servers may receive sensitive information, including coin keys or private inputs required to create proofs. If those services are compromised or operated by untrusted providers, users could face serious security risks, including unauthorized access to assets.
Blessing-Hartley recommended local proof generation using WebAssembly, locally operated proof servers, or trusted providers using secure execution environments.
Indexing services present a separate concern. Viewing keys allow software to inspect relevant shielded transactions, so access to those keys must also be protected.
He then distinguished between publicly visible and shielded asset transfers.
Ordinary unshielded transactions expose information such as sender and recipient addresses, transferred amounts, and token identities.
Shielded transactions conceal those details while still leaving certain accounting information visible, including activity involving the shielded pool and the number of coin records entering or leaving it.
Smart contract interactions create additional metadata.
Observers may be able to identify which application was called, the public name of the executed function, and information written to the blockchain during execution.
This creates a potential weakness when developers use descriptive function names such as mint, transfer, or registerSession.
Blessing-Hartley reported that an examination of contracts on Midnight Preprod and mainnet allowed him to infer the purpose of nearly every application he reviewed, with only two or three exceptions, largely through publicly visible function names.
He suggested that developers consider neutral function names or generic entry points, such as API, where privately handled parameters determine the actual operation.
Repeated labels, recognizable transfer amounts, and predictable transaction sequences can also make individual activities easier to correlate.
To demonstrate the issue, Blessing-Hartley shared observations from active Midnight contracts.
One unidentified application, which he called App A, recorded 12,754 contract calls within 24 hours.
He suspected much of that activity was generated by automated software rather than thousands of independent users. The figures did not establish how many people were actually interacting with the application.
Nevertheless, he considered the application's less descriptive function names a positive feature because they revealed relatively little about its purpose.
Other contracts were easier to interpret. Examples included applications associated with temperature logging, data anchoring, session registration, and voting.
Voting applications were particularly relevant because identifying voting-related activity could encourage attempts to distinguish participants and correlate their subsequent actions.
Such analysis does not necessarily reveal someone's real-world identity. It can, however, expose patterns of behavior that users expected to remain private.
[NEWSBREAK]
Why Spartacus, Anonymity Pools and Quantum Security Matter
Blessing-Hartley's third major theme was the anonymity set, the group of possible participants among whom an observer cannot easily identify a particular user's activity.
"Blend in with the crowd."
He explained that hiding transaction values is not sufficient if an individual is the only person performing a recognizable action.
During the presentation, he reported that approximately 32,000 shielded coins had been minted on Midnight mainnet.
That figure referred to coin records rather than unique users. It also did not mean that every application automatically benefited from an anonymity set of that size.
When users interact with individual smart contracts, the relevant group of indistinguishable participants may become dramatically smaller.
This is particularly problematic when launching a new decentralized application.
With few users and limited transaction activity, the first interactions are relatively easy to distinguish and potentially follow over time.
Blessing-Hartley delivered one of the presentation's strongest warnings:
"Your first user is identifiable forever as that individual."
His point concerned the ability to recognize and track a particular participant's activity, even without knowing their actual name or identity.
The issue also helps explain the 12,754 calls observed in App A. High activity can complicate transaction analysis, but only when the surrounding patterns make individual actions genuinely difficult to distinguish.
To help developers address this challenge, Blessing-Hartley introduced Spartacus, a tool he plans to publish as open-source software through Shielded Technologies.
Spartacus is intended to generate additional smart contract calls and exercise application endpoints, creating a broader set of activity around real user interactions.
During development, he encountered practical challenges involving automated bots and the use of Midnight's test tokens on Preprod, which he indicated he had largely resolved.
The objective is to make specific activities less conspicuous, particularly in applications that would otherwise have very little transaction volume.
He also suggested a more straightforward alternative: bringing a large group of people into an application and encouraging continued participation.
However, neither automated activity nor additional users automatically guarantee anonymity. Distinctive transaction patterns, public metadata, or recognizable automation can still allow observers to separate different types of activity.
Blessing-Hartley plans to release Spartacus publicly and seek feedback from other developers. He did not provide a launch date or present independently verified measurements of its effectiveness.
The discussion then turned to longer-term cryptographic security.
Blessing-Hartley confirmed that Shielded Technologies is working on improvements intended to protect Midnight against the threat commonly described as harvest now, decrypt later.
Under this scenario, attackers collect encrypted information today and store it in anticipation of future computing advances that could make decryption possible.
He referenced differing predictions about the development of sufficiently powerful quantum computers, including estimates involving 2029, without presenting any timeline as certain.
He characterized quantum attacks as a long-term concern rather than an immediate emergency, while emphasizing the importance of preparing existing systems before such threats become practical.
Some of the protective measures he discussed, including careful handling of hashes and sensitive data, can reduce current information exposure. They do not, by themselves, constitute a complete quantum-resistant cryptographic solution.
Blessing-Hartley closed by returning to the fundamental responsibilities of developers: verify user claims, minimize disclosure, protect sensitive keys, and ensure that users are not unnecessarily distinguishable through application activity.
He also reiterated the need to assess AI-generated code against explicit security requirements before deployment.
For teams already building on Midnight mainnet, those recommendations translate into specific engineering checks covering contract endpoints, transaction patterns, proof servers, indexers, key management, and the treatment of private information.
Spartacus is intended to address one part of that broader challenge. Blessing-Hartley's next stated step is to publish the tool as open-source software so developers can examine its behavior, contribute improvements, and test whether generated contract activity provides meaningful anonymity benefits.