Peter Bui Warns of Tampered Ledger Devices
Bui examines reports of hidden hardware implants and fraudulent Ledger emails, alongside the wallet practices he uses for Cardano transactions.
By SongMarketCap
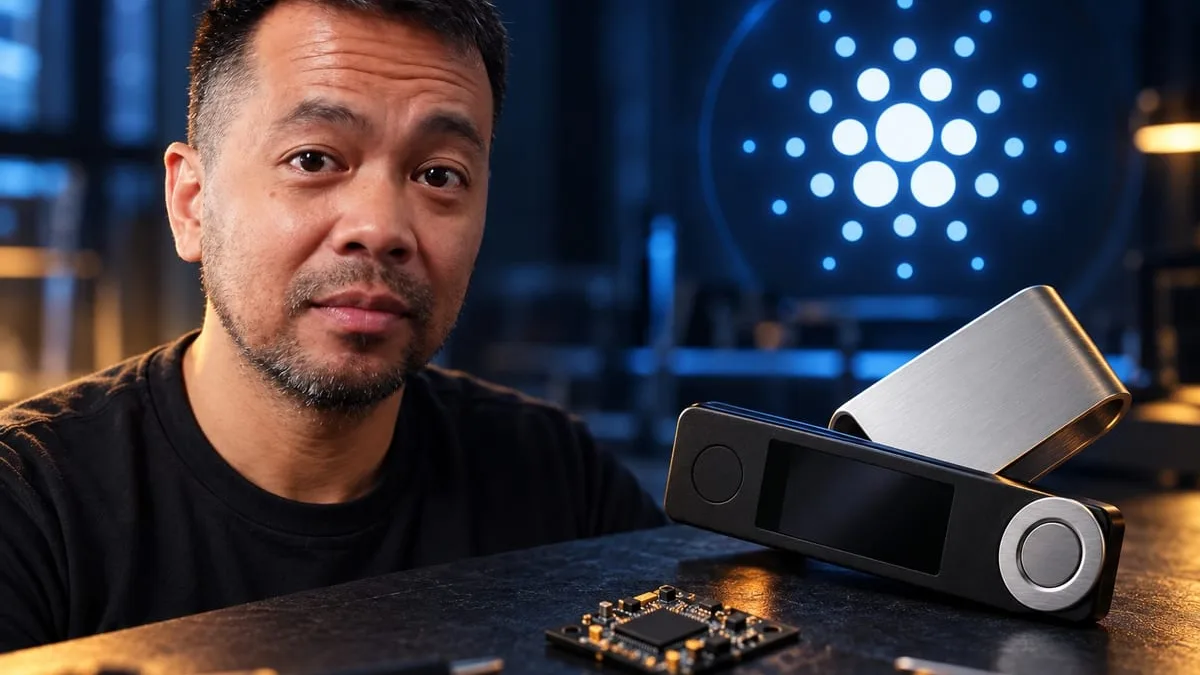
Peter Bui don warn about reports of theft wey involve Ledger hardware wallets wey dem physically modify, and e talk say losses fit reach about $80 million for im video. Im gist focus on devices wey Southeast Asian retailer wey dem dey call CryptoBilis sell and how recovery phrases fit don leak, one security concern wey concern holders of ADA and other crypto assets.
Hidden Hardware in Ledger Wallets
Based on posts from former Mt. Gox CEO Mark Karpelès and other community members, Bui review photographs of extra electronic assembly wey dem see inside Ledger Nano devices.
E describe one module wey get eSIM component wey fit transmit information go give attacker. Im explanation link the suspected implant to possible exposure of sensitive wallet data, including recovery phrases. The mechanism na how im take account the investigation reach.
Poor soldering, residual flux, and scratched-off chip markings appear for im examination of the photographs. Bui interpret the removed markings as attempt to hide the component identity.
Im account follow investigators effort to check whether the problem pass devices wey dem sell for Southeast Asia, before attention later focus on CryptoBilis. E still relay one claim say public disclosure alert the attackers, and dem later drain compromised wallets. That sequence na part of the information wey e recount, no be finding wey dem independently establish for the video.
A Fraudulent Ledger Email Adds Another Threat
The discussion shift from physical devices to impersonation when Bui show one email wey e receive that morning. The email present itself as Ledger security notification and e mention threats wey relate to new AI models. When dem check the sender, e show Hive Management instead of the expected Ledger identity.
The example show the phishing scenario wey e describe: one security warning wey look legit create urgency, direct the recipient go fraudulent website, and encourage installation of supposed update.
Bui connect this kind targeted messages to earlier breach of Ledger customer information. According to im explanation, exposed email addresses give scammers way to reach people wey dem know say get hardware wallets.
E recommend make people buy directly from the manufacturer to reduce risks wey dey associated with intermediaries. Im email example address another point of exposure after purchase, when impersonator go try gain the owner trust.
Cardano Signing and Offline Storage
For im own Cardano transactions, including delegated representative activities, Bui dey use Keystone hardware wallet. QR code signing na the practical advantage wey e emphasize, e talk say e easy pass to dey work through lengthy transactions with repeated button presses on Ledger.
E still advocate make wallet hardware, firmware, and software dey more open so people fit examine their design. As e dey discuss Keystone, e disclose say e dey receive commissions through affiliate links wey dey below the video.
Paper wallets appear as another option to keep access credentials offline, including for ADA holdings. Bui describe dem as potentially the safest option for that moment and e mention encrypting private keys. This one remain im personal assessment; the video no demonstrate how to set dem up or compare storage methods with security testing.
As e return to the suspected implants, Bui urge Ledger owners make dem inspect their devices and e promise links to identification materials. Im closing warning concern the interval between exposure and theft: credentials fit don already compromise while funds still untouched, fit leave attacker with ability to act later.